NetCloudz PKI
Launching soonYour own certificate authority, made in Europe.
An API-first certificate authority from a Dutch company, for organizations that need to issue, manage, and revoke their own X.509 certificates — for TLS, mutual TLS, device identity, and internal services. A clean browser UI for operators, a complete REST API and ACME automation for machines, and every key, token, and signing operation treated as a crown jewel.
A European product
Private PKI from a European company.
Built in the Netherlands
NetCloudz PKI is developed by NetCloudz B.V., a Dutch company based in Utrecht. You deal directly with the people who build it, under a European company.
You decide where it runs
Run it on-premises or in your own cloud account, in the region you choose, so your keys and certificate data stay where your policies require.
Ready for your European reviews
Append-only audit trails, role-based access and exportable logs give you evidence for your own NIS2 and GDPR reviews.
Three principles
Security
Key material, tokens, and signing operations are treated as crown jewels. Private keys are encrypted at rest with AES-256-GCM. Least privilege, defense in depth, and fail-closed defaults throughout — including an offline signing ceremony for root key operations.
Compliance
Behavior is auditable and verifiable. Crypto choices track current best practice (RFC 5280, RFC 8555). Full audit trails, and revocation semantics that are never weakened for convenience.
Operational ease
Designed to run 24/7 across many tenants and issuers. Safe roll-forward and roll-back migrations, predictable restarts, discoverable configuration, and observability (logs, metrics, audit) that gives on-call enough to diagnose without a debugger.
For decision-makers
What it does and why it matters — no deep technical background required.
Own your trust, end to end
Run your own Root and Issuer certificate authorities in-house. Certificates for your internal services, devices, and people are issued under your authority, on your terms. Issue as many certificates as you need, with no dependence on an external vendor and no sensitive names leaking into public certificate logs.
Automate renewals, prevent expiry outages
A common and avoidable cause of internal outages is an expired certificate nobody was watching. NetCloudz PKI supports ACME — the same automation standard used by the public web — so applications request and renew their own certificates automatically. The service can even renew its own TLS certificate without operator involvement.
Built for audit and compliance
Every security-relevant action — issuance, revocation, login, key export, configuration change — is recorded in an append-only audit trail. Logs are scoped by role, retained for a configurable period, and exportable to CSV or JSON for compliance reviews and incident investigations.
Least-privilege access by default
Bring your existing identity provider (Microsoft Entra ID, Keycloak, Auth0, or any standard OIDC provider) for single sign-on, with group memberships synced automatically. Add multi-factor authentication for sensitive accounts. Fine-grained roles and groups ensure people only manage the certificates they are entitled to.
Designed for air-gapped trust
For organizations whose policy requires the Root CA keys to never touch a networked machine, NetCloudz PKI ships an offline ceremony tool. The Root key stays entirely air-gapped while the online service handles day-to-day issuance under intermediate authorities — the standard arrangement for protecting your most valuable key.
Operate it 24/7 with confidence
A self-service browser UI for operators, built-in health checks for orchestrators, Prometheus metrics for your existing monitoring, and safe, reversible database upgrades. It is designed to be boring to run: predictable restarts, discoverable configuration, and enough observability to diagnose issues without a debugger.
Recover from the worst day
Documented backup, restore, and key-rotation procedures mean a leaked or lost encryption key, a failed host, or a compromised intermediate are recoverable events with a runbook — not existential ones.
See it in action
A browser UI for operators on top of the API — here are a few of the screens you and your team work in.
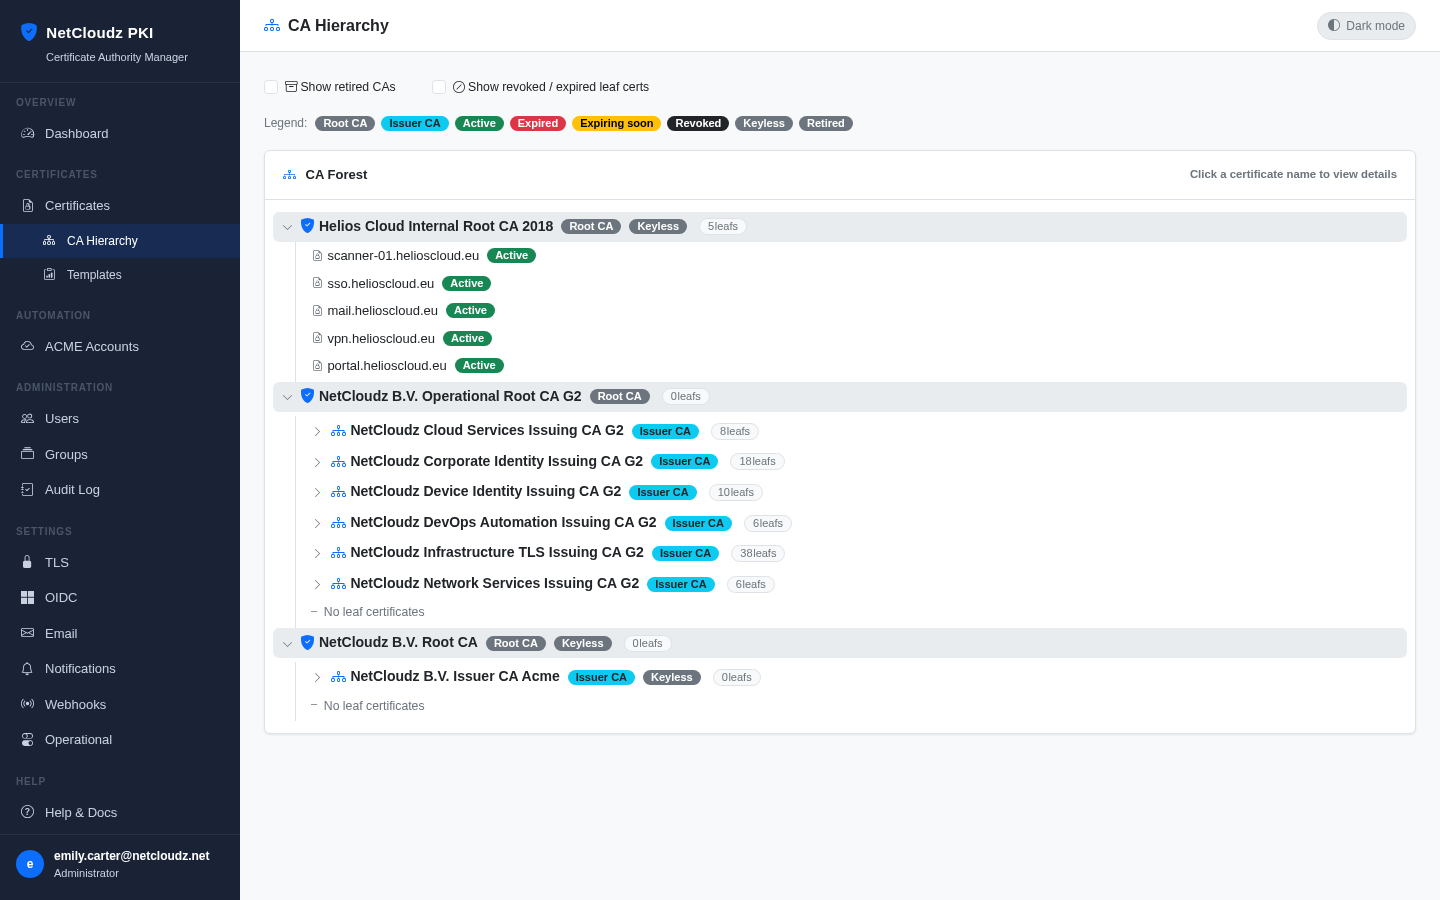
See your entire trust hierarchy
The full Root → Issuer → leaf forest in one view — offline roots, per-business-unit issuing CAs, and imported chains, each with status and expiry.
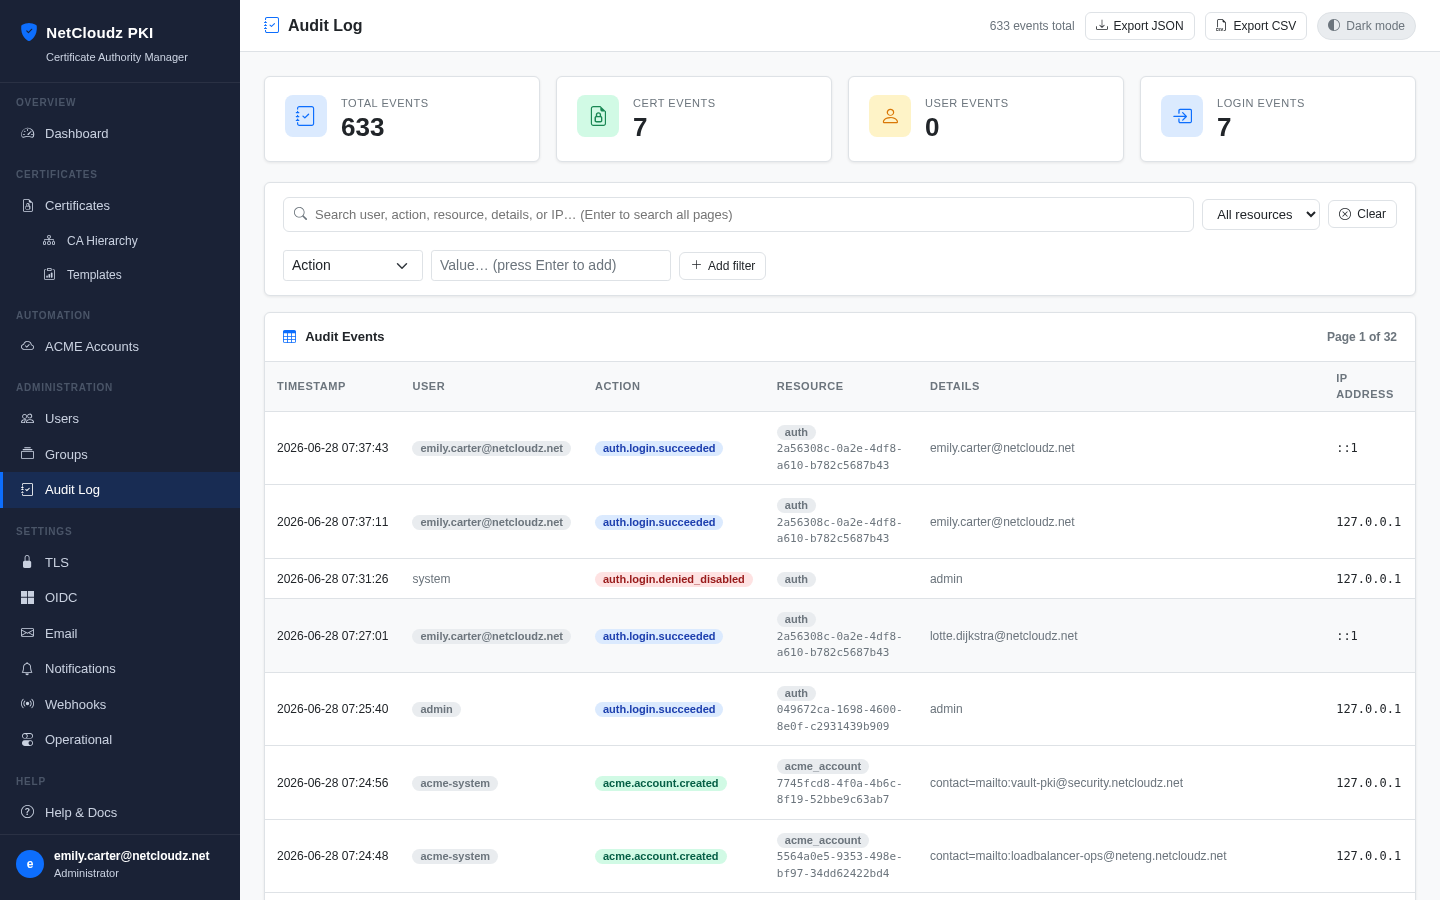
A complete, searchable audit trail
Every security-relevant action — logins, issuance, revocation — recorded, filterable, and exportable to CSV or JSON for compliance.
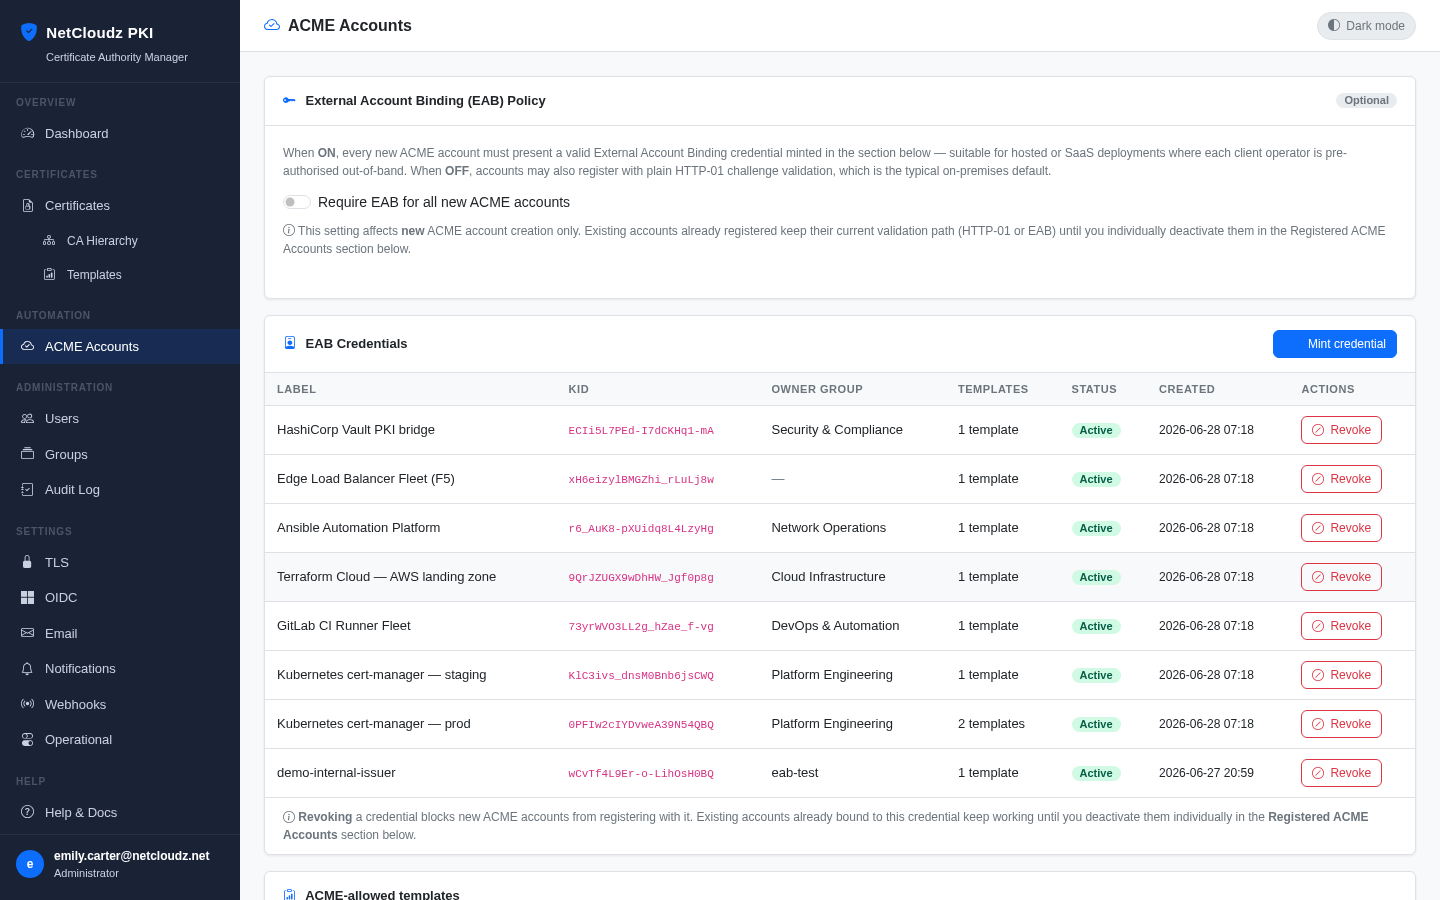
Automation with ACME and EAB
Register ACME accounts, gate access with External Account Binding, and scope each credential to specific certificate templates.
What's inside
X.509 hierarchies
Root CA → Issuer CA → Client certificates, fully managed.
ACME automation
Automated issuance and renewal per RFC 8555.
REST API + browser UI
API-first, with a full management UI on top.
OIDC SSO
Single sign-on for operators via OpenID Connect.
CRL & OCSP
Public, rate-limited revocation endpoints.
Keys encrypted at rest
AES-256-GCM with key rotation support.
Audit log
Every security-relevant action is recorded.
Offline ceremony
Air-gapped root key generation and signing.
How you run it
Same product, your choice of who keeps it running — a fully managed service, or self-hosted on-premises or in your own AWS or Azure account, in the region you choose, with implementation support from our team.
Fully managed
We build it. We run it. You operate it.
We host and operate NetCloudz PKI as a service. You manage your certificate authorities, certificates, and users through the API and browser UI — we take care of the infrastructure, upgrades, and uptime.
Self-hosted
We build it. You run it. You operate it.
Run NetCloudz PKI in your own environment — on-premises, or in your own AWS or Azure account in the region you choose. Full deployment documentation is included, and our team offers hands-on implementation support to integrate it into your infrastructure.
Evaluating the architecture?
Standards, crypto, the CA hierarchy, ACME, revocation, and operations — all in one technical reference.
On the roadmap
What's coming next
Planned capabilities, not available yet — where NetCloudz PKI is headed.
Post-quantum certificate support
Issuance with post-quantum and hybrid signature algorithms as the standards finalize, so your hierarchy is ready for the migration before it becomes urgent.
MCP server
A Model Context Protocol server so AI assistants and agents can query and manage certificates through the same roles, audit trail, and guardrails as everyone else.
Terraform provider
Manage certificate authorities, templates, and certificates as code — declare your PKI in Terraform and roll it out through your existing infrastructure pipelines.
See it in your environment
Request a demo and we'll show NetCloudz PKI against your hierarchy and issuance workflow.
Request a demo